Aiden for InfraOps - Agentic Infrastructure Lifecycle Management

Ship infra at AI speed

Aiden for InfraOps turns a developer request into Terraform or OpenTofu, built from your approved modules, checked against your policies, and queued for approval before anything reaches your cloud.

Aiden for InfraOps: dithered isometric blocks with orange accents
 
SELF-SERVICE
Developers ask in their own tools

No ticket queue and no context switch. Requests come from IDEs, coding agents, from the CLI over MCP, or from ServiceNow when a system of record is required.

STANDARDIZED
Every request builds on your modules

Aiden starts from your curated golden module catalog, so what a developer receives is the pattern your platform team already approved, emitted as standard Terraform or OpenTofu.

GUARDRAILS
Policy is checked before deployment

OPA policy runs at generation time, not after the fact. Non-compliant infrastructure is rejected with the reason and the fix, before anything reaches your cloud.

SELF SERVICE FOR DEVELOPER VELOCITY

From intent to infrastructure.

Aiden turns developer infrastructure requests into Terraform or OpenTofu, with policy checks and team approval before deployment.
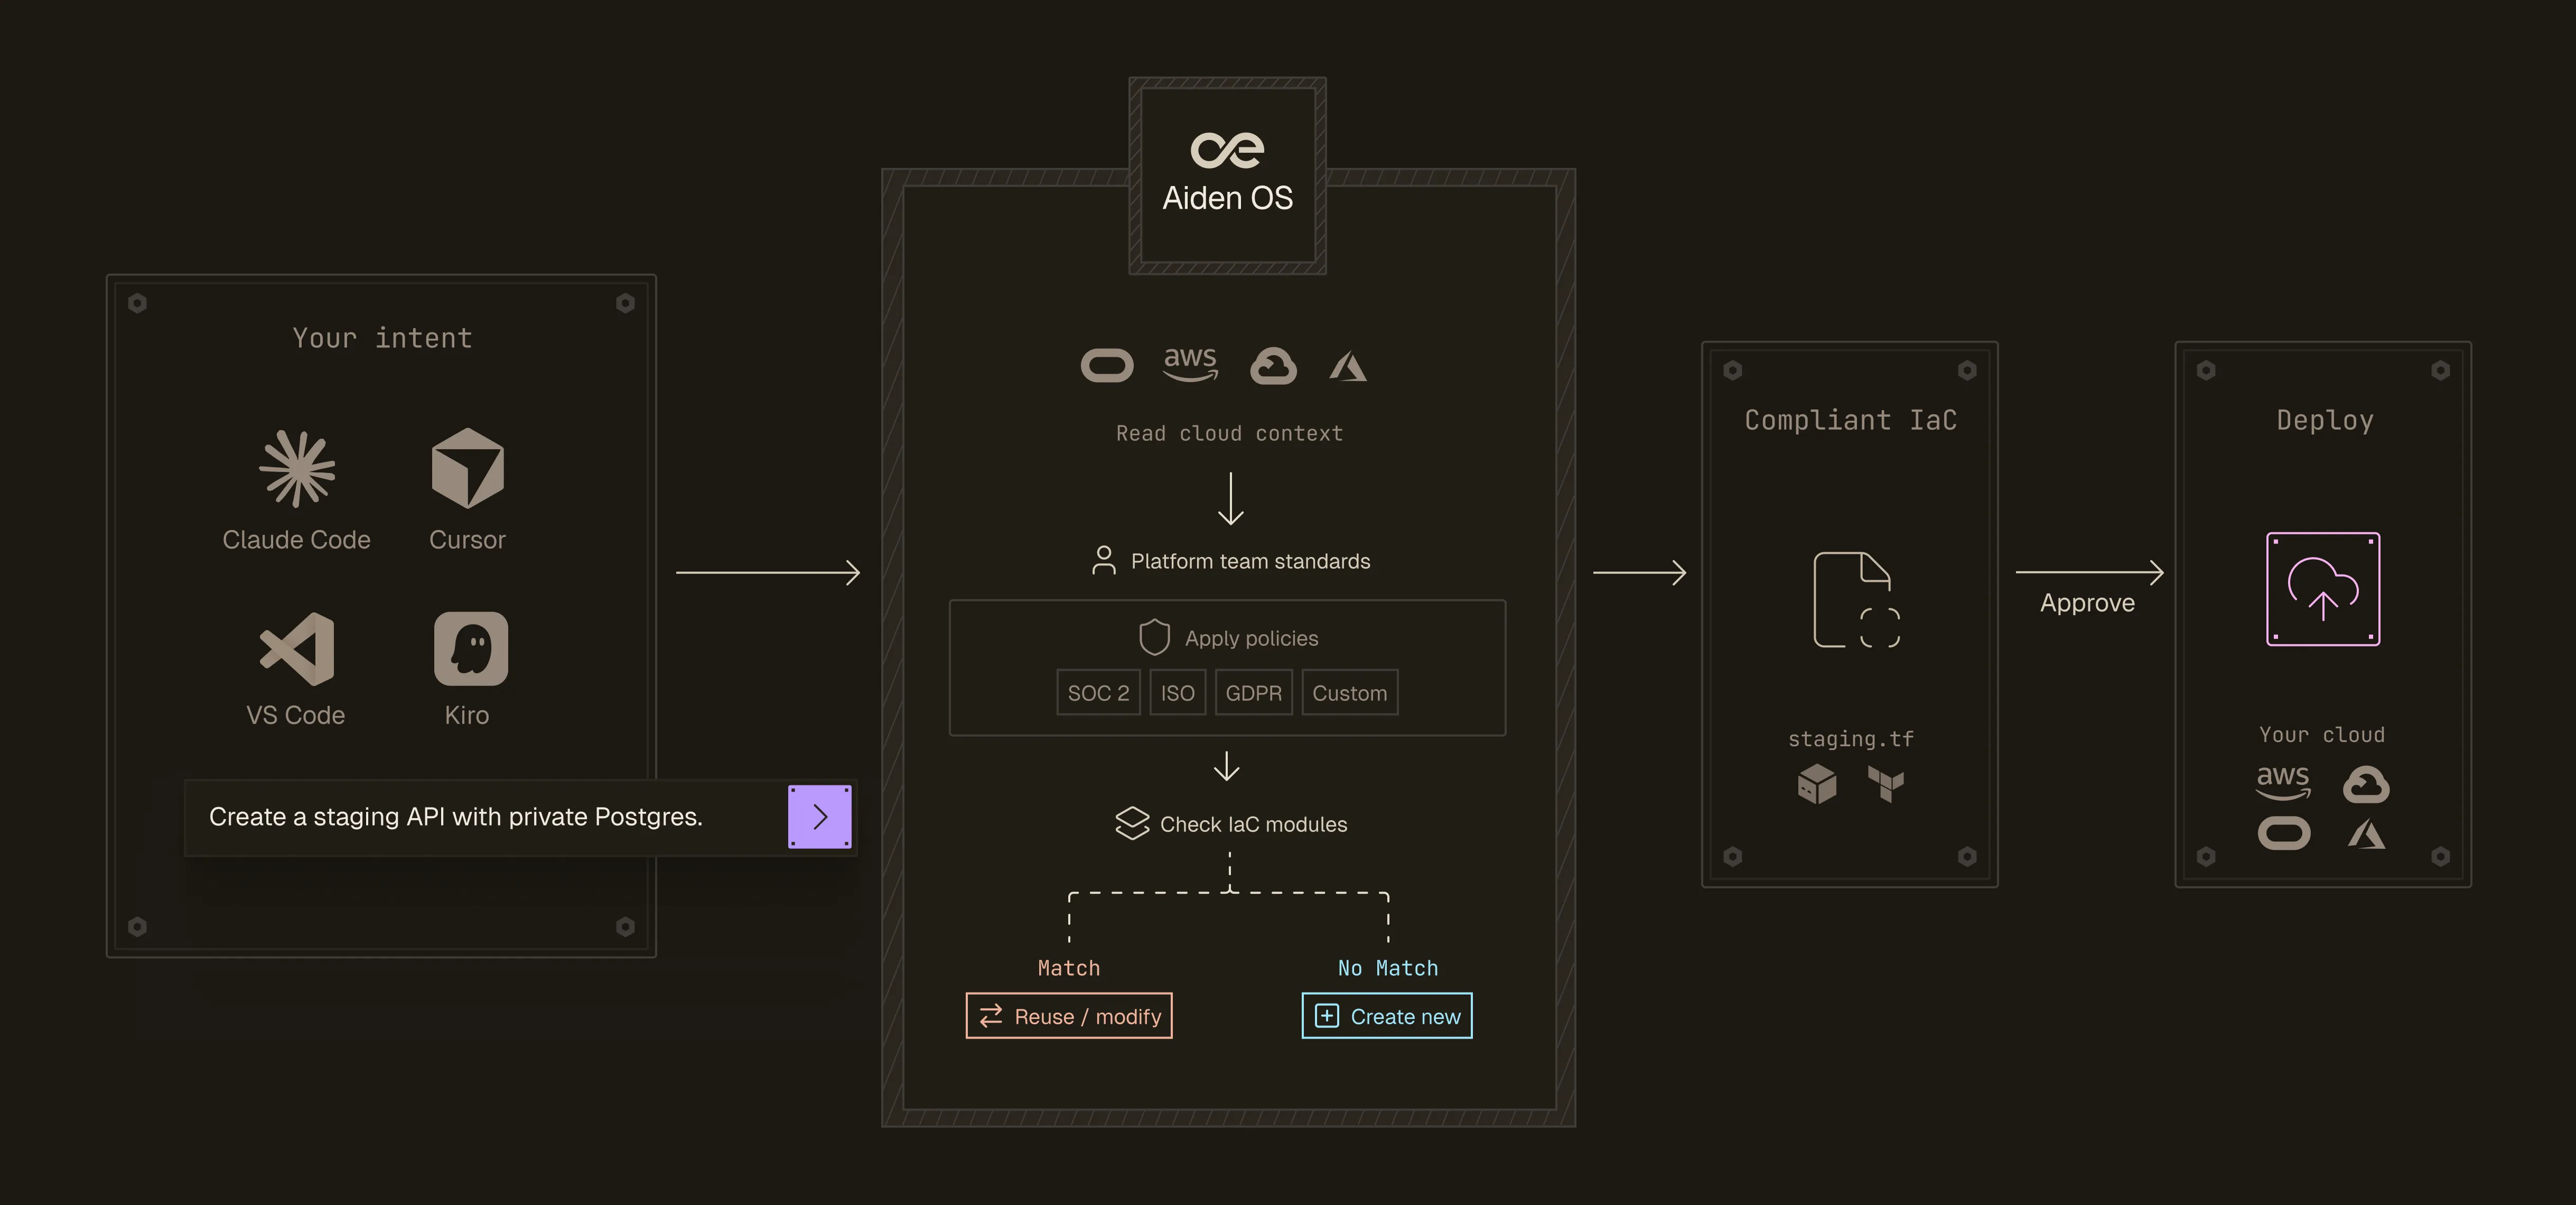
Aiden OS flow from developer intent through platform standards to compliant IaC and deploy
Meet application devs where they are.
MCP
Coding agents
Backstage
Aiden for InfraOps Now available as a Kiro Power

Go from plain-English developer intent to a production-ready, security-hardened application on Amazon Web Services (AWS)

Know More
INFRASTRUCTURE STANDARDIZATION

Discover existing infrastructure.
Build on approved modules.
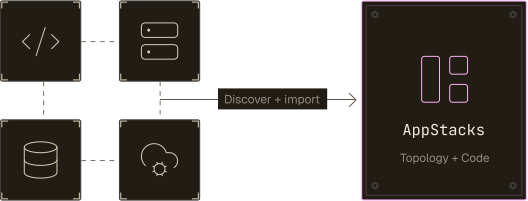
Bring what’s already running through Cloud Asset Discovery.
Discover your existing infrastructure and bring its topology andcode into one workspace.
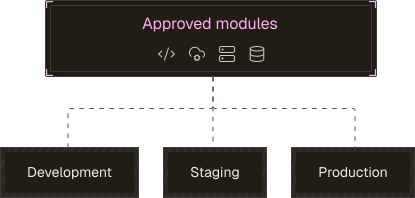
Build once. Reuse your standards.
Aiden starts with your approved modules, so teams build on thepatterns you trust.
INFRASTRUCTURE GUARDRAILS

Infrastructure that conforms to your security and compliance policies.

Aiden checks proposed IaC against your security and compliance policies, blocking noncompliant changes before deployment.

BUILT IN  COMPLIANCE FRAMEWORKS
SOC 2
PCI DSS
HIPAA
FedRAMP
GDPR
NIST 800-53
NIST 800-171
NIST CSF
MARS-E
Enforced by OPA at generation time, with IaC scanning built in and via Wiz.
INFRASTRUCTURE LIFECYCLE MANAGEMENT

Day 0 through day 2, in one control plane

Generating infrastructure is the easy half. Aiden also imports what is already running, watches it for drift, and keeps a record of who changed what.

DAY 0
Discover

Import Terraform and OpenTofu state to inventory brownfield and ClickOps estates. No rip-and-replace.

DAY 0
Design

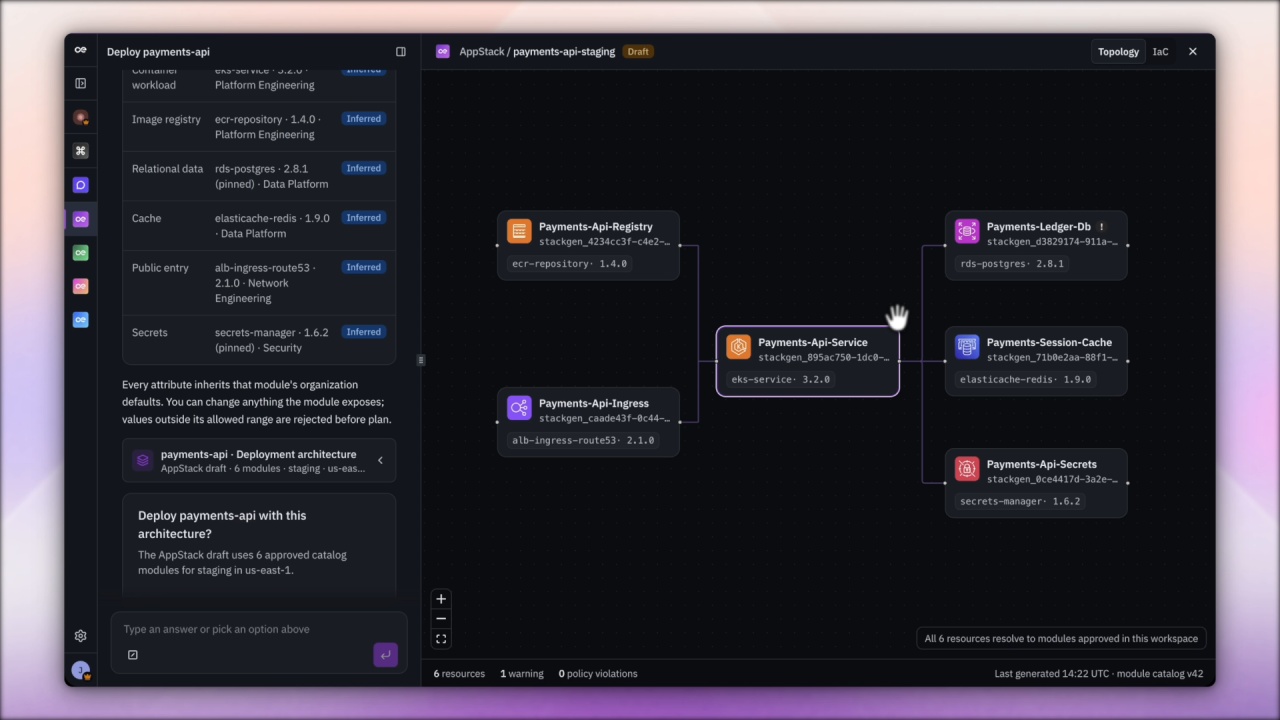
Organize resources on a topology canvas and package them into appStacks by team and project workspace.

DAY 1
Provision

Requests become policy-checked IaC, held for approval, then applied through centrally governed remote runs.

DAY 2
Detect drift

Live cloud resources are compared continuously against defined IaC state, usable as a CI/CD pipeline gate.

DAY 2
Govern

RBAC at enterprise, project and user scope, with audit and activity logs for every deployment and change.

faq

Frequently Asked Questions

How does Aiden ensure my infrastructure follows our security and compliance requirements?
Can Aiden work with our existing InfraOps and tools?
What happens if Aiden makes a mistake or I need to modify the generated infrastructure?
How much infrastructure knowledge do developers need to use Aiden effectively?
How does Aiden for InfraOps differ from Aiden for DevOps?

See your infrastructure workflow with Aiden

Book a Demo
×

Download the brochure

Complete the form to get your copy.