Shift Left Security Scanning for Infrastructure
Identify security violations early with Wiz IaC scanning built into your StackGen infrastructure workflows
StackGen is trusted by leading enterprises





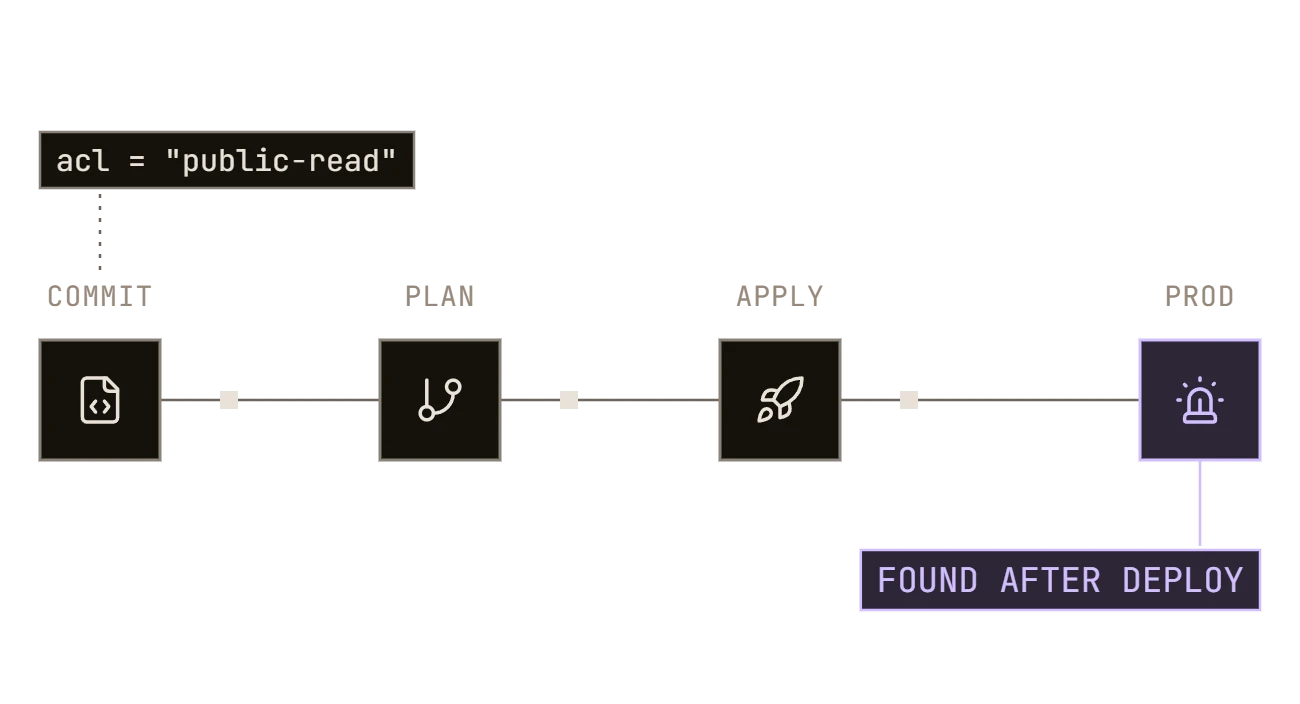
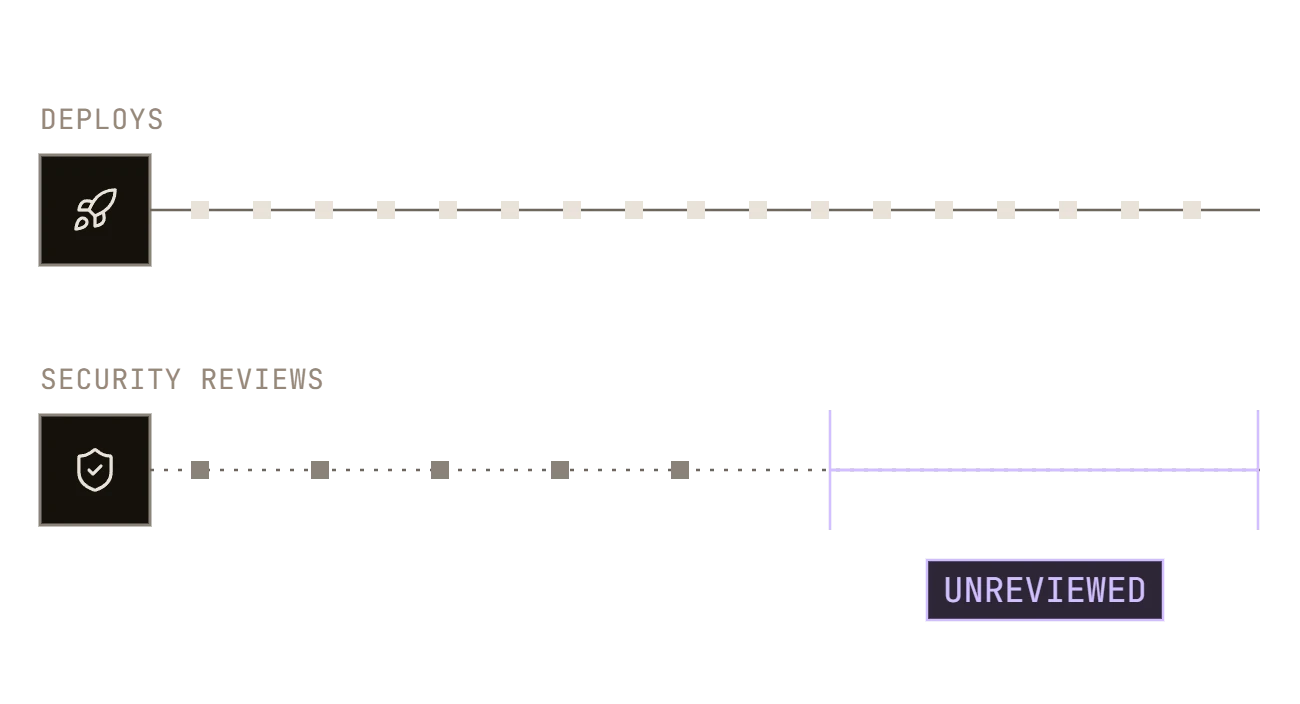
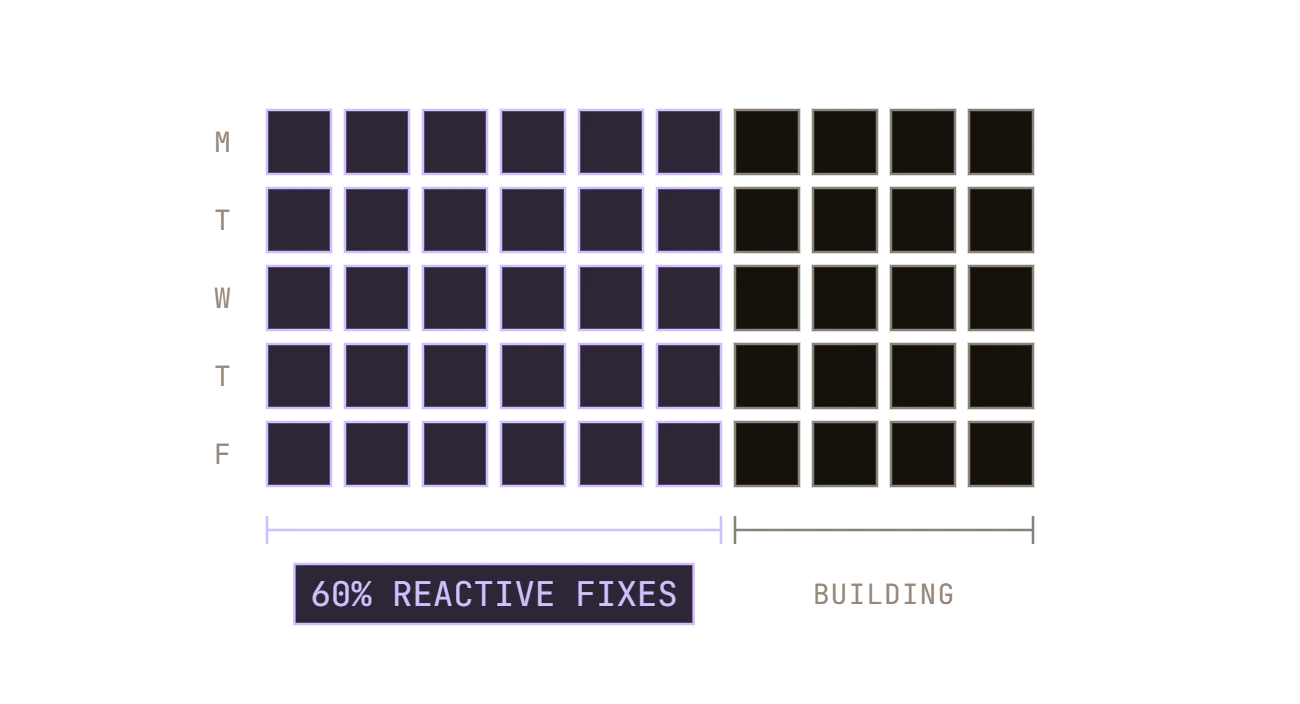
Reactive Security Is Costing You More Than You Think
Powerful Security Enforcement Capabilities from Wiz
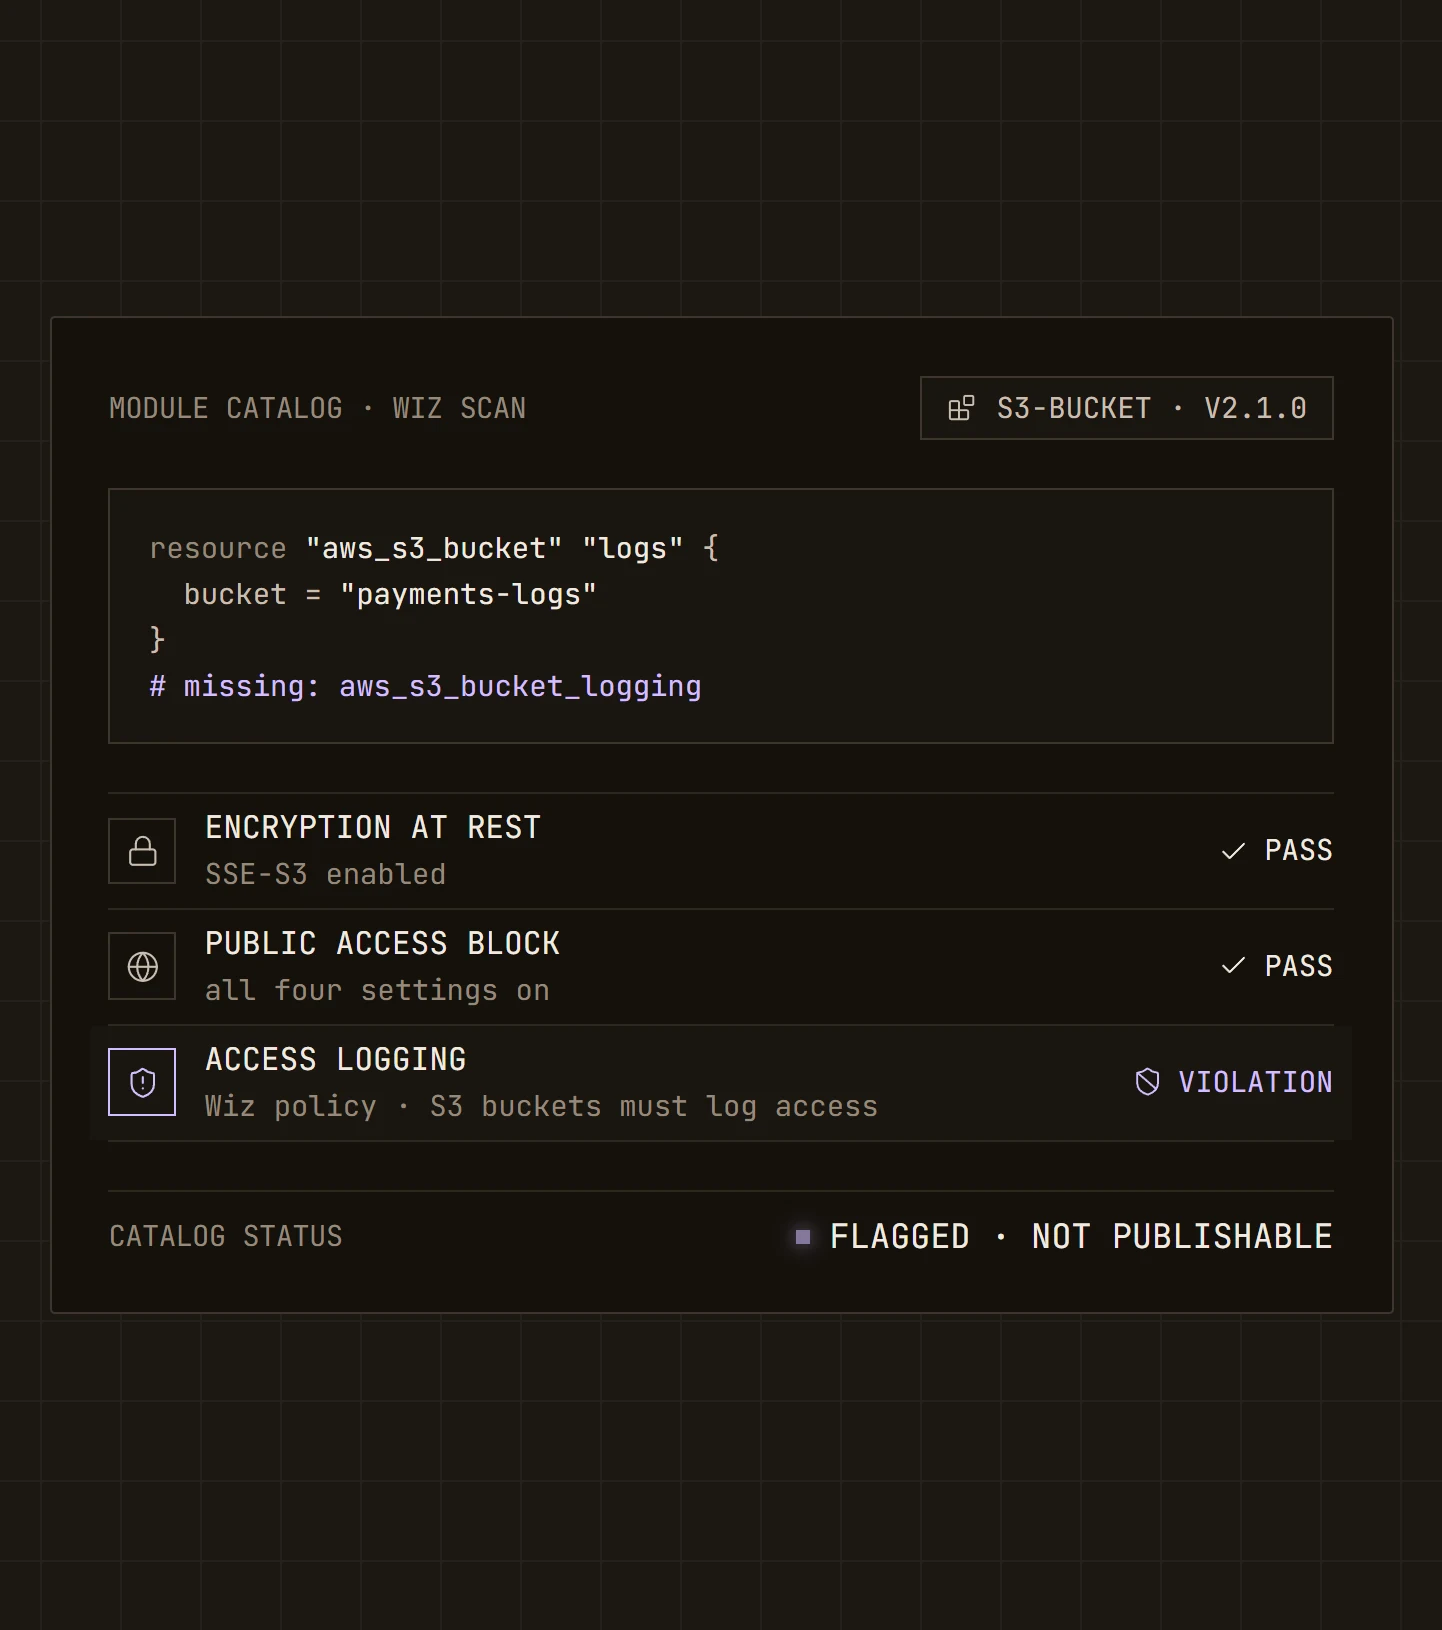
IaC Level
For example, Wiz policy requires all S3 buckets to have logging enabled for security and compliance. If any Terraform module in the StackGen catalog defines an S3 resource without logging, Wiz flags it as a violation.
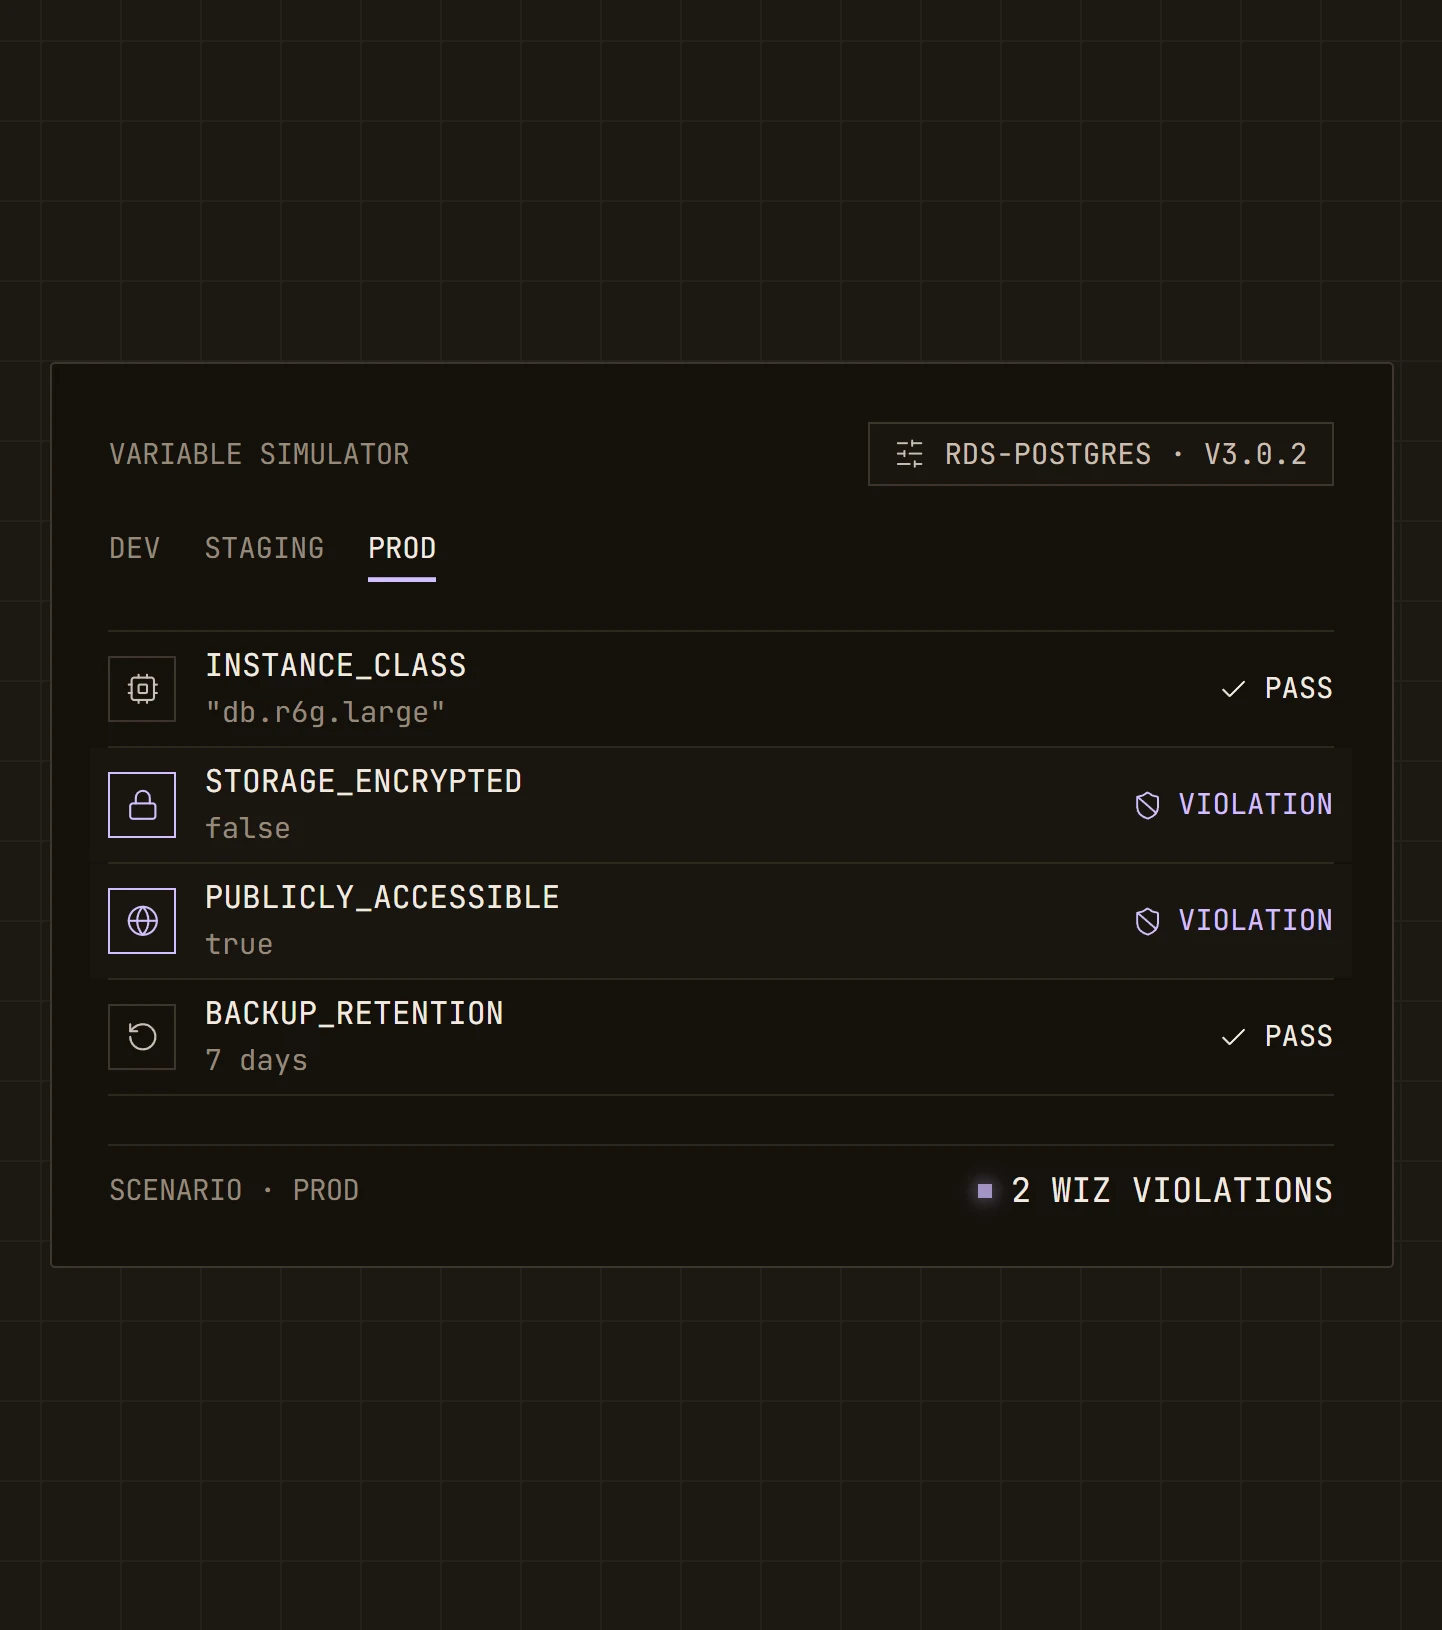
Variable Level
StackGen provides a Simulator UI that allows developers to test variable values across different scenarios.
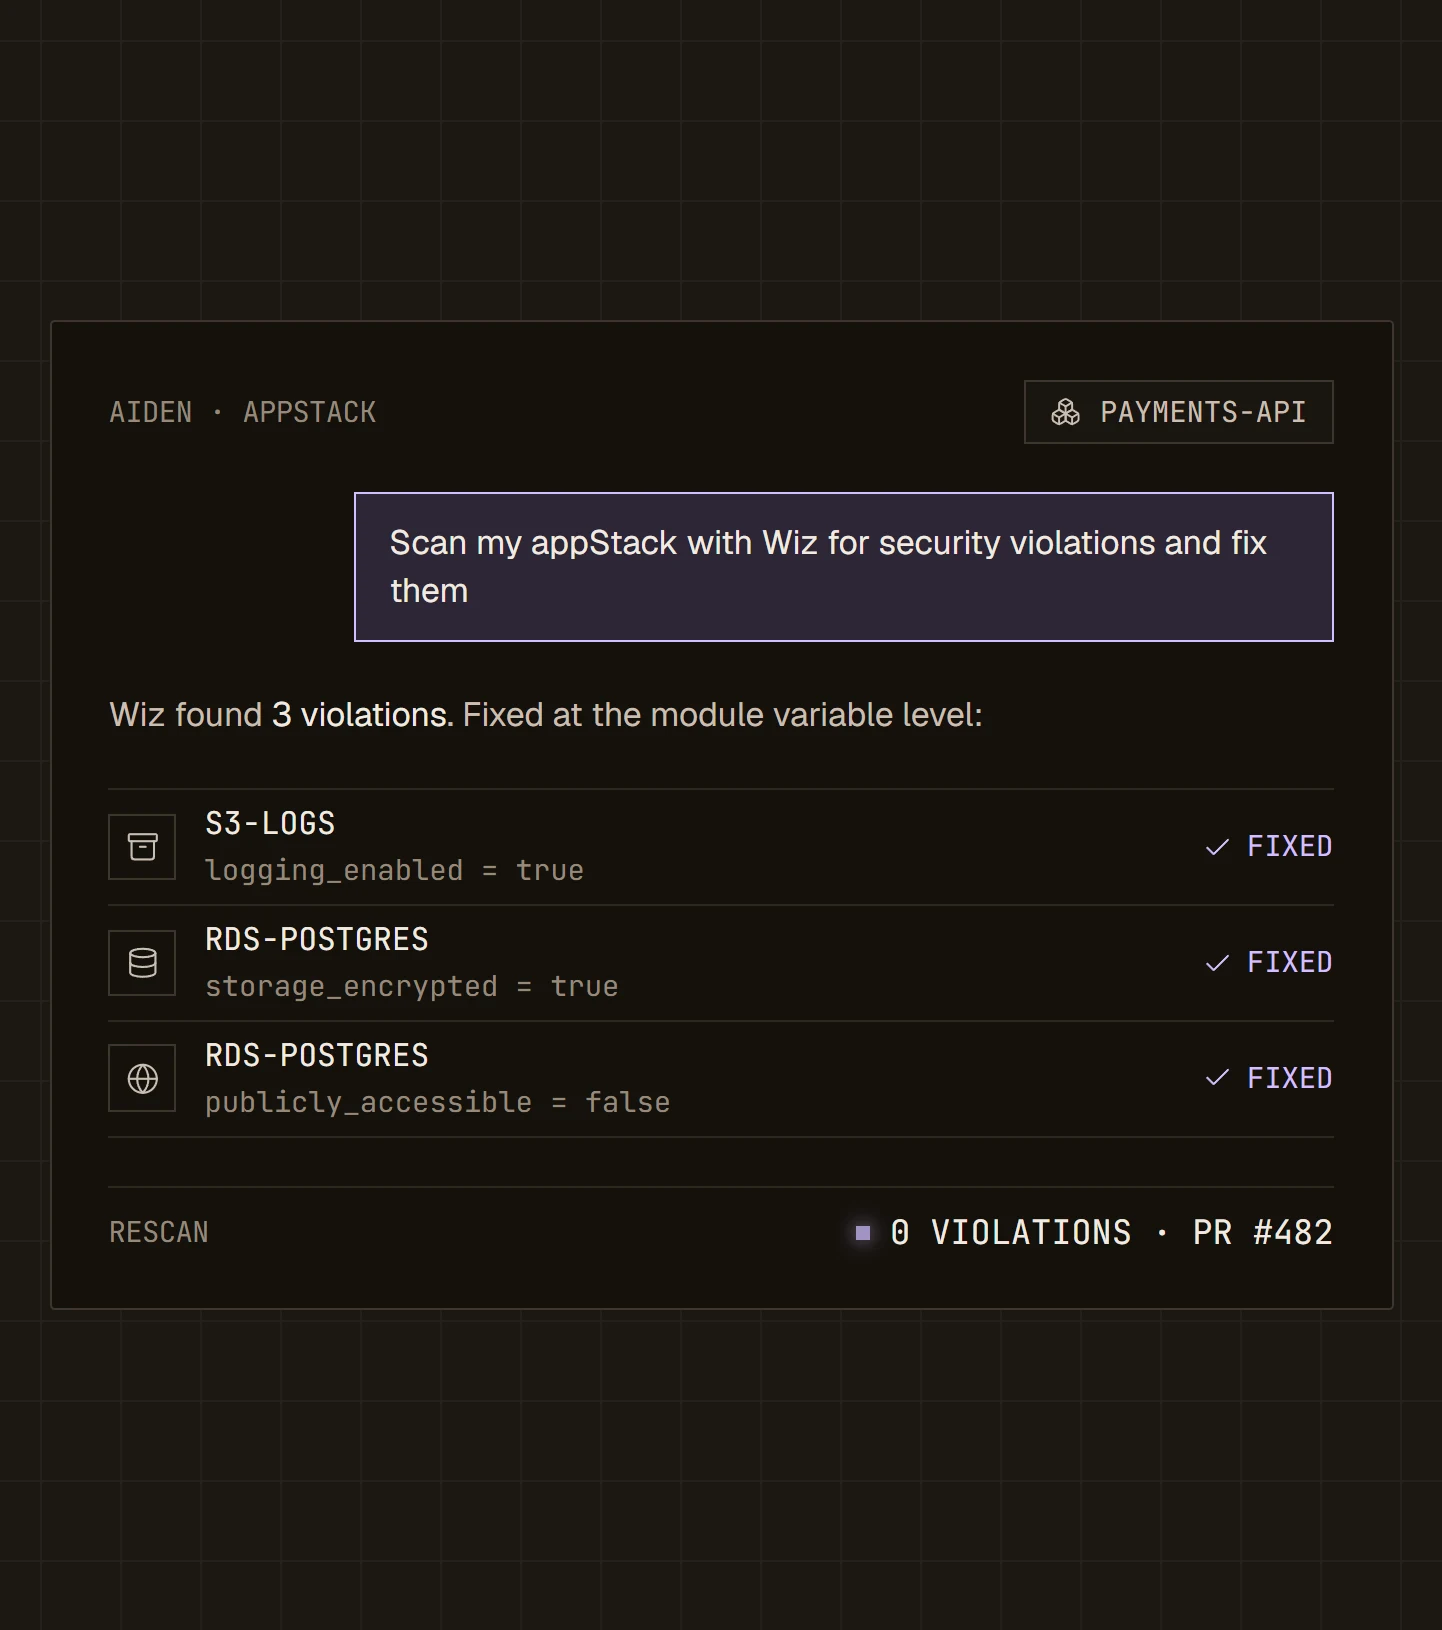
"Scan my appStack with Wiz for security violations and fix them"
Aiden has the same Wiz integration abilities to scan StackGen appStack IaCs and make Terraform module variable level fixes
Prevent Security Issues Before They Reach Production
Reduce security incidents by 80% with pre-deployment scanning
Catch Terraform module vulnerabilities before they reach production—preventing costly misconfigurations and breaches.
Cut remediation time by 60% with centralized compliance visibility
View Wiz violations directly in your Module Catalog—helping platform engineers prioritize and fix critical issues faster.
Ship secure infrastructure 3x faster without slowing developers
Enable shift-left security with AppStack-level alerts—maintaining development velocity while enforcing compliance standards.